Chrome //
Extensions
 Chrome
Web store
Disable Content-Security-Policy Chrome Extension


-
Chrome Extension Page
-
Total Number of Extension users:60K +
-
Reviewed by :82 Chrome Users
-
Author Name:
-
['True', 'Phil Grayson']
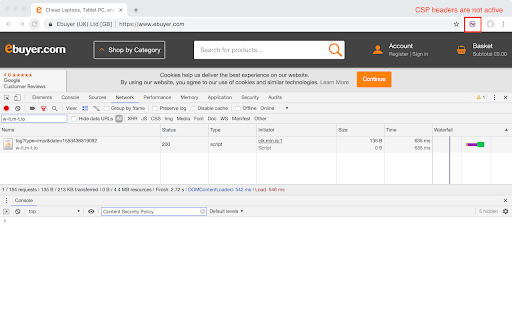
 Use at your own risk. This disables the Content-Security-Policy header for a tab. Use this when testing what resources a new third-party tag includes onto the page.

Click the extension icon to disable Content-Security-Policy header for the tab. Click the extension icon again to re-enable Content-Security-Policy header.

Use this only as a last resort. Disabling Content-Security-Policy means disabling features designed to protect you from cross-site scripting. Prefer to use report-uri which instructs the browser to send CSP violations to a URI. That allows you keep Content-Security-Policy enabled in your browser but still know what got blocked. https://report-uri.com is a free tool that gives you a web interface to inspect CSP violations on your site.
How to install Disable Content-Security-Policy chrome extension in chrome Browser
You can Follow the below Step By Step procedure to install the Disable Content-Security-Policy Chrome Extension to your Chrome Web browser.
- Step 1: Go to the Chrome webstore https://chrome.google.com/webstore or download the extension Disable Content-Security-Policy Chrome Extension Download from https://pluginsaddonsextensions.com
- Step 2: Now search for the Disable Content-Security-Policy in Chrome Webstore Search and click on the search button.
- Step 3: click on the Disable Content-Security-Policy Chrome Extension Link
- Step 4: in the next page click on the Add to Chrome button to Download and Install the Disable Content-Security-Policy extension for your Chrome Web browser .
Disable Content-Security-Policy Chrome extension Download
Looking for a method to Disable Content-Security-Policy Download for Chrome then this download link is for you.It is the Disable Content-Security-Policy Chrome extension download link you can download and install Chrome Browser.
Download Disable Content-Security-Policy chrome extension (CRX)
-
Automatically generate content security policy headers online for any website.
-
Always Disable Content-Security-Policy for web application testing. When the icon is colored, CSP headers are disabled.
-
CSP Evaluator is a tool that allows developers to check if a Content Security Policy (CSP) serves as mitigation against XSS attacks.
-
Drops X-Frame-Options and Content-Security-Policy HTTP response headers, allowing all pages to be iframed.
-
Allows the user to modify requests as they happen.
-
Easily remove CSP (Content-Security-Policy) rules from the response header.
-
No more CORS error by appending 'Access-Control-Allow-Origin: *' header to local and remote web requests when enabled
-
Modify the Content Security Policy of web pages.
-
Easily add (Access-Control-Allow-Origin: *) rule to the response header.
-
The easiest way to Redirect URLs, Modify HTTP Headers, Mock APIs, Inject custom JS, Modify GraphQL Requests